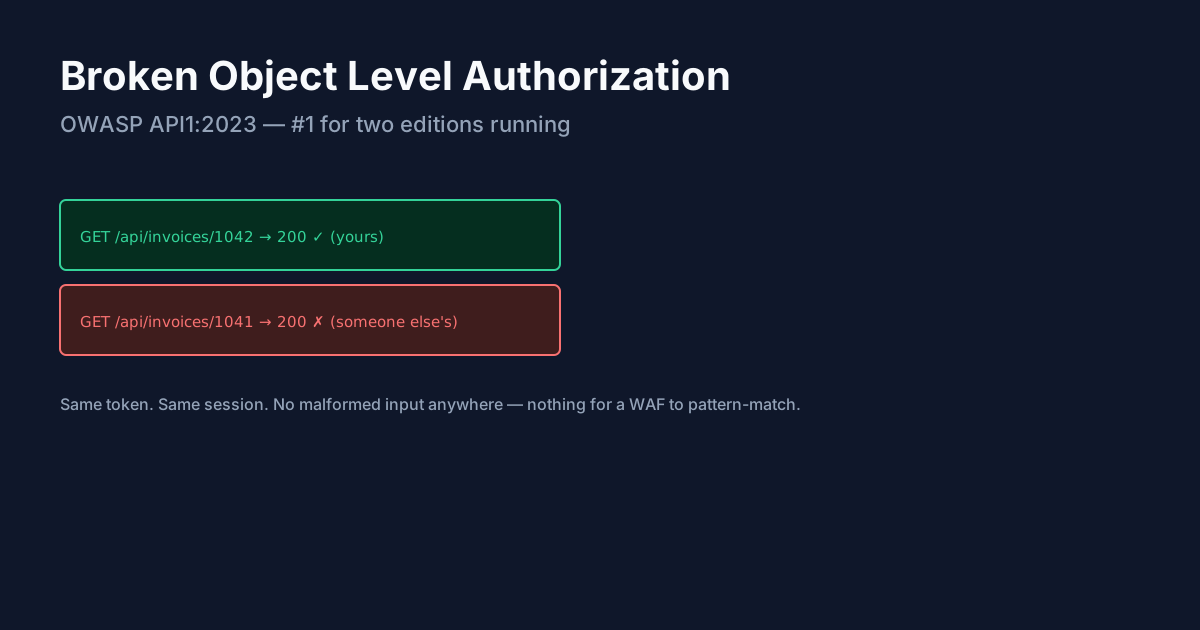
Your API's biggest hole isn't injection - it's the ID in the URL
Broken Object Level Authorization has been OWASP's #1 API risk across two consecutive editions, and it's invisible to WAFs, schema validators, and most scanners - because the request is perfectly well-formed. Here's why BOLA is structurally different from injection, and what actually stops it in 2026.
Sep 16, 202610 min read